Cyber Security Engineer & CTO
AmrHamdy.
I break web apps, APIs and networks for a living, then help teams fix them. 5+ years of offensive security across Egypt and the UAE, now leading technology at Tawwan.
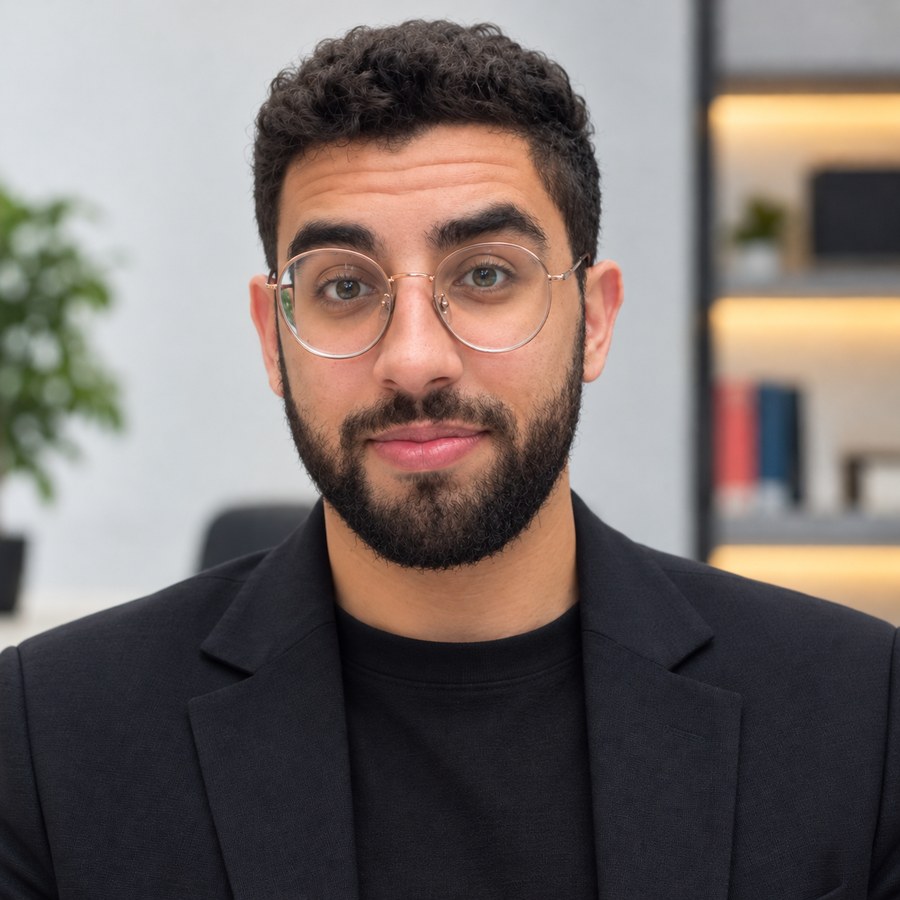
Amr Hamdy · AngixBlack
years in offensive security
GitHub stars on Corscan
Companies · Tools · Platforms
 Tawwan
 El Motahida
 Aurages
 Focal PointAngixBlackTawwanEl MotahidaAuragesFocal PointAngixBlackTawwanEl MotahidaAuragesFocal PointAngixBlackTawwanEl MotahidaAuragesFocal PointAngixBlack
Offensive mindset. Defensive responsibility.
I'm a Cyber Security Engineer combining independent bug bounty research since 2021 with professional penetration testing, application security and engineering leadership in Egypt and the UAE.
My speciality is web application, REST API and network penetration testing — finding, exploiting and remediating OWASP Top 10 issues such as XSS, SQL injection, IDOR, broken authentication, access-control and business-logic flaws.
Today I'm CTO of Tawwan, a platform I architected and built end to end. Before that I led engineering for AI-powered and digital-forensics products, enforcing a secure SDLC across teams.
Based in
Lithuania — available across the EU and remotely
Languages
Arabic (native) · English (professional) · Lithuanian (learning)
Focus areas
04Offensive Security
Pentesting, red team ops, adversary simulation, exploit development, privilege escalation, Active Directory attacks.
Application Security
Web & API testing, OWASP Top 10 / ASVS, secure code review, threat modeling, Secure SDLC.
AI & LLM Security
Prompt injection & jailbreaks, OWASP Top 10 for LLM apps, AI agent & RAG security, MITRE ATLAS.
Leadership
Team leadership, technical mentoring, security awareness training, client communication.
What I can do for your team.
Engagements I run end to end, from scoping to a report your developers and executives can both act on.
Web & API Penetration Testing
Manual, business-logic-aware testing of web apps and REST APIs against OWASP Top 10 and ASVS, with CVSS-rated findings and proof of concept.
Network & Infrastructure Testing
External and internal network assessments, Active Directory attack paths, hardening and vulnerability-management guidance.
Secure Code Review & AppSec
Code review, threat modeling and Secure SDLC design so vulnerabilities are caught before they ship.
AI & LLM Security Assessment
Prompt-injection, jailbreak, agent and RAG testing aligned with OWASP Top 10 for LLM applications and MITRE ATLAS.
Security Training & Awareness
Hands-on workshops for developers and staff, from secure coding to social-engineering resistance.
Fractional CTO / Security Lead
Technical leadership for startups: architecture, secure-by-design delivery and launch readiness.
Where I've built, broken and secured things.
Five roles across product engineering and offensive security.
- Jun 2026 — Present
Chief Technology Officer (CTO)
- Lead technology strategy, architecture and hands-on development of Tawwan, an Arabic omnichannel inbox and comment-automation SaaS platform.
- Architected and built the platform end to end, including Meta and Google API integrations and AI-driven automation workflows.
- Apply secure-by-design principles across the product: authentication, authorisation, data protection, secrets management and secure deployment.
- Own the technical roadmap, infrastructure and launch readiness; work directly with the business side on product direction and investor discussions.
ArchitectureMeta & Google APIsAI automationSecure by design - Sep 2025 — May 2026
Tech Lead
El MotahidaCairo, Egypt- Led the software development department, owning planning, design and delivery of complex software solutions.
- Combined team management with hands-on engineering on the architecture and code of AI-powered and digital-forensics products.
- Enforced secure coding standards and structured code reviews across all projects; designed systems for resilience and reliability.
- Embedded security controls into every stage of the SDLC together with cybersecurity teams; mentored developers.
AI productsDigital forensicsSecure SDLCMentoring - Jan 2025 — Aug 2025
Cyber Security Engineer
- Performed web application and REST API penetration tests on client and internal systems using manual techniques and automated scanning.
- Identified, exploited and documented critical vulnerabilities: XSS, SQL injection, IDOR, broken authentication, session-management and business-logic flaws.
- Automated reconnaissance, scanning and validation with Burp Suite, OWASP ZAP, Nmap and custom Python scripts.
- Delivered reports with CVSS-based risk ratings, proof-of-concept evidence and remediation guidance; re-tested fixes with development teams.
Web & API pentestingBurp SuiteOWASP ZAPCVSS reporting - Jun 2023 — Jul 2024
Software Engineer
Focal PointDubai, UAE- Designed, built and maintained the company's web platforms end to end: custom WordPress themes and plugins, hosting, performance optimisation and backups.
- Conducted security assessments of websites, web servers and network infrastructure and implemented controls to protect sensitive data.
- Hardened web servers and CMS installations: access control, patching, WAF configuration, file-permission and plugin auditing.
- Worked with the IT team to prioritise and remediate vulnerabilities and strengthen overall security posture.
Full-stackWordPressHardeningWAF - 2021 — Present
Independent Security Researcher · Bug Bounty Hunter
- Research and report vulnerabilities in public bug bounty and responsible-disclosure programmes across web applications and APIs.
- Focus on CORS misconfigurations, open redirects, XSS, IDOR and authentication / access-control flaws.
- Developed and open-sourced recon and detection tooling (Corscan, RedirXploit, Kid Recon, gitools) to scale research.
CORSOpen redirectXSSIDORTooling
Products I lead. Tools I open-sourced.
From a SaaS platform to recon tooling used by bug bounty hunters.
Graduation project · PHP
Surveillance Camera E-Commerce
Designed and built the PHP/MySQL backend: product catalogue, order management and secure user authentication.
Core competencies
What I use every week, grouped by discipline.
Offensive Security
- Penetration Testing
- Vulnerability Assessment
- Red Team Operations
- Adversary Simulation
- Bug Bounty
- Exploit Development
- Privilege Escalation
- Active Directory Attacks
- Social Engineering
Application Security
- Web & API Pentesting
- OWASP Top 10
- OWASP ASVS
- Secure Code Review
- Threat Modeling
- AuthN / AuthZ Testing
- Secure SDLC
AI & LLM Security
- LLM App Security Testing
- OWASP Top 10 for LLM
- Prompt Injection
- Jailbreak Attacks
- AI Agent & RAG Security
- MITRE ATLAS
Network & Infrastructure
- Network Pentesting
- Firewalls
- IDS / IPS
- Hardening
- Linux & Windows Administration
- Vulnerability Management
Forensics & Intelligence
- Digital Forensics
- Incident Response
- OSINT
- Malware Analysis
Leadership
- Team Leadership
- Technical Mentoring
- Project Planning
- Security Awareness Training
- Technical Report Writing
- Client Communication
Tools & technologies
27Certifications, training & education
Credentials earned and professional courses completed.
Certifications
Professional training
Education
Highlights
INE / eLearnSecurity
03- eWPTX — Web App Penetration Tester eXtreme
- eWPT — Web App Penetration Tester
- eJPTv2 — Junior Penetration Tester
OffSec
02- OSEP — Experienced Penetration Tester
- OSCP — Certified Professional
EC-Council
02- CEH v13 — Certified Ethical Hacker
- Ethical Hacking Essentials (EHE)
ITI — Information Technology Institute
01- Certified Ethical Hacker (CEH)
APIsec University
01- API Penetration Testing
American Board
01- Penetration Testing
Teaching Planet Academy
01- Certificate of Experience in Hacking
Education
Bachelor of Management Information Systems (MIS)
Giza Institute — Giza, Egypt
Arabic (native) · English (professional) · Lithuanian (learning)
Let's secure something together.
Need a penetration test, an application security review, or a technical leader for your product? I'd love to hear from you.
Replies within 24 hours